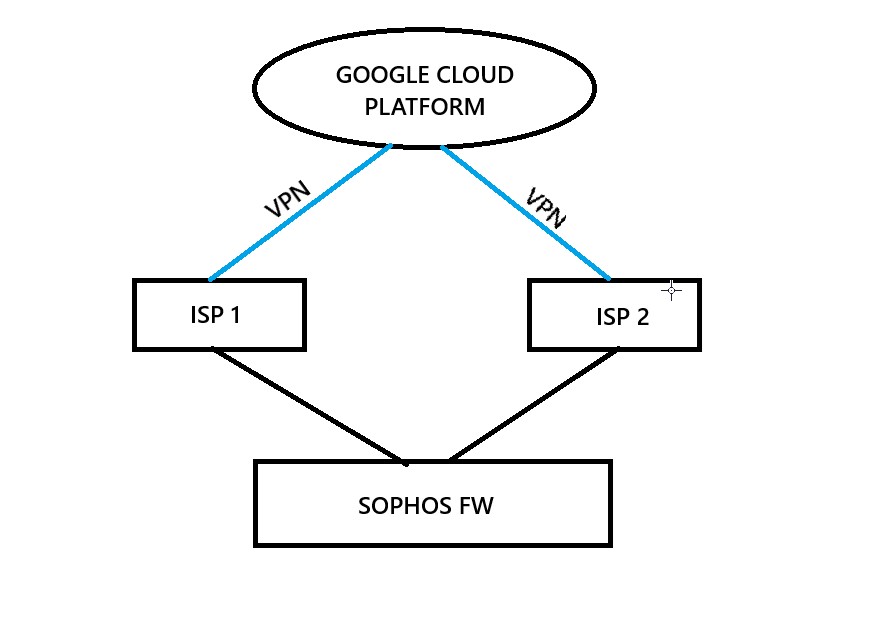
Hi, how can we configure Peplink if we have 2 ISPs and each of these is connected to Google Cloud Platform via VPN?
we using Sophos XGS Firewall for VPN connection
Hi, how can we configure Peplink if we have 2 ISPs and each of these is connected to Google Cloud Platform via VPN?
we using Sophos XGS Firewall for VPN connection
image shown is the actual network topology. If we place the Peplink above the firewall, how can we connect VPN to both ISPs?
Can anyone give me an idea? Appreciate your help.
It depends. what do you want to achieve? I mean why are you looking at the Peplink?
I would assume for reliable VPN to GCP? If so run a FusionHub in GCP, put the peplink on the WAN of the Sophos, it becomes your internet router and builds a bonded VPN to GCP, then you can simply route from the WAN of the sophos to your GCP networks.
What we want to try is the 2 vpn/failover si still handled by Sophos, and Peplink works as an internet load balancer.
What sessions do you plan to load balance? VPN tunnels are a single session so they can’t be load balanced, you can fail them over so if one ISP link fails you redirect the VPN tunnel that was on that WAN to the other WAN.