BR2 Pro – requirement feasibility check

Please let me know if the BR2 Pro can support the setup below, and how you would configure it.

Situation:

  • I am receiving one Ethernet port carrying two tagged 802.1Q VLANs. Each VLAN is a separate transport. Traffic sent back out on this port must keep the same VLAN IDs.
  • I am also using two 5G SIMs, bonded together, as a backup transport.
  • A downstream router sits behind the BR2 Pro. It will make all routing and failover decisions across the two VLAN transports and the 5G backup, and it marks DSCP values on its packets for QoS.

Questions:

  1. Can the BR2 Pro terminate the two VLANs on one physical port as two separate transports?

  2. Can the two 5G SIMs be bonded as one backup transport? Is a SpeedFusion peer or FusionHub required for this?

  3. Can the two VLAN transports and the bonded 5G backup each be handed off separately to the downstream router, with the BR2 Pro never moving traffic from one transport to another on its own?

  4. Can the two VLAN transports run without NAT, so the downstream router’s IP addresses are visible at the far end?

  5. Can MTU of 1700 bytes be supported on the two VLAN transports?

  6. DSCP:
    a) Does the BR2 Pro forward DSCP values unchanged, in both directions, on the two VLAN transports?
    b) Can the original DSCP value be copied to the tunnel’s outer header, and if so how is it enabled?
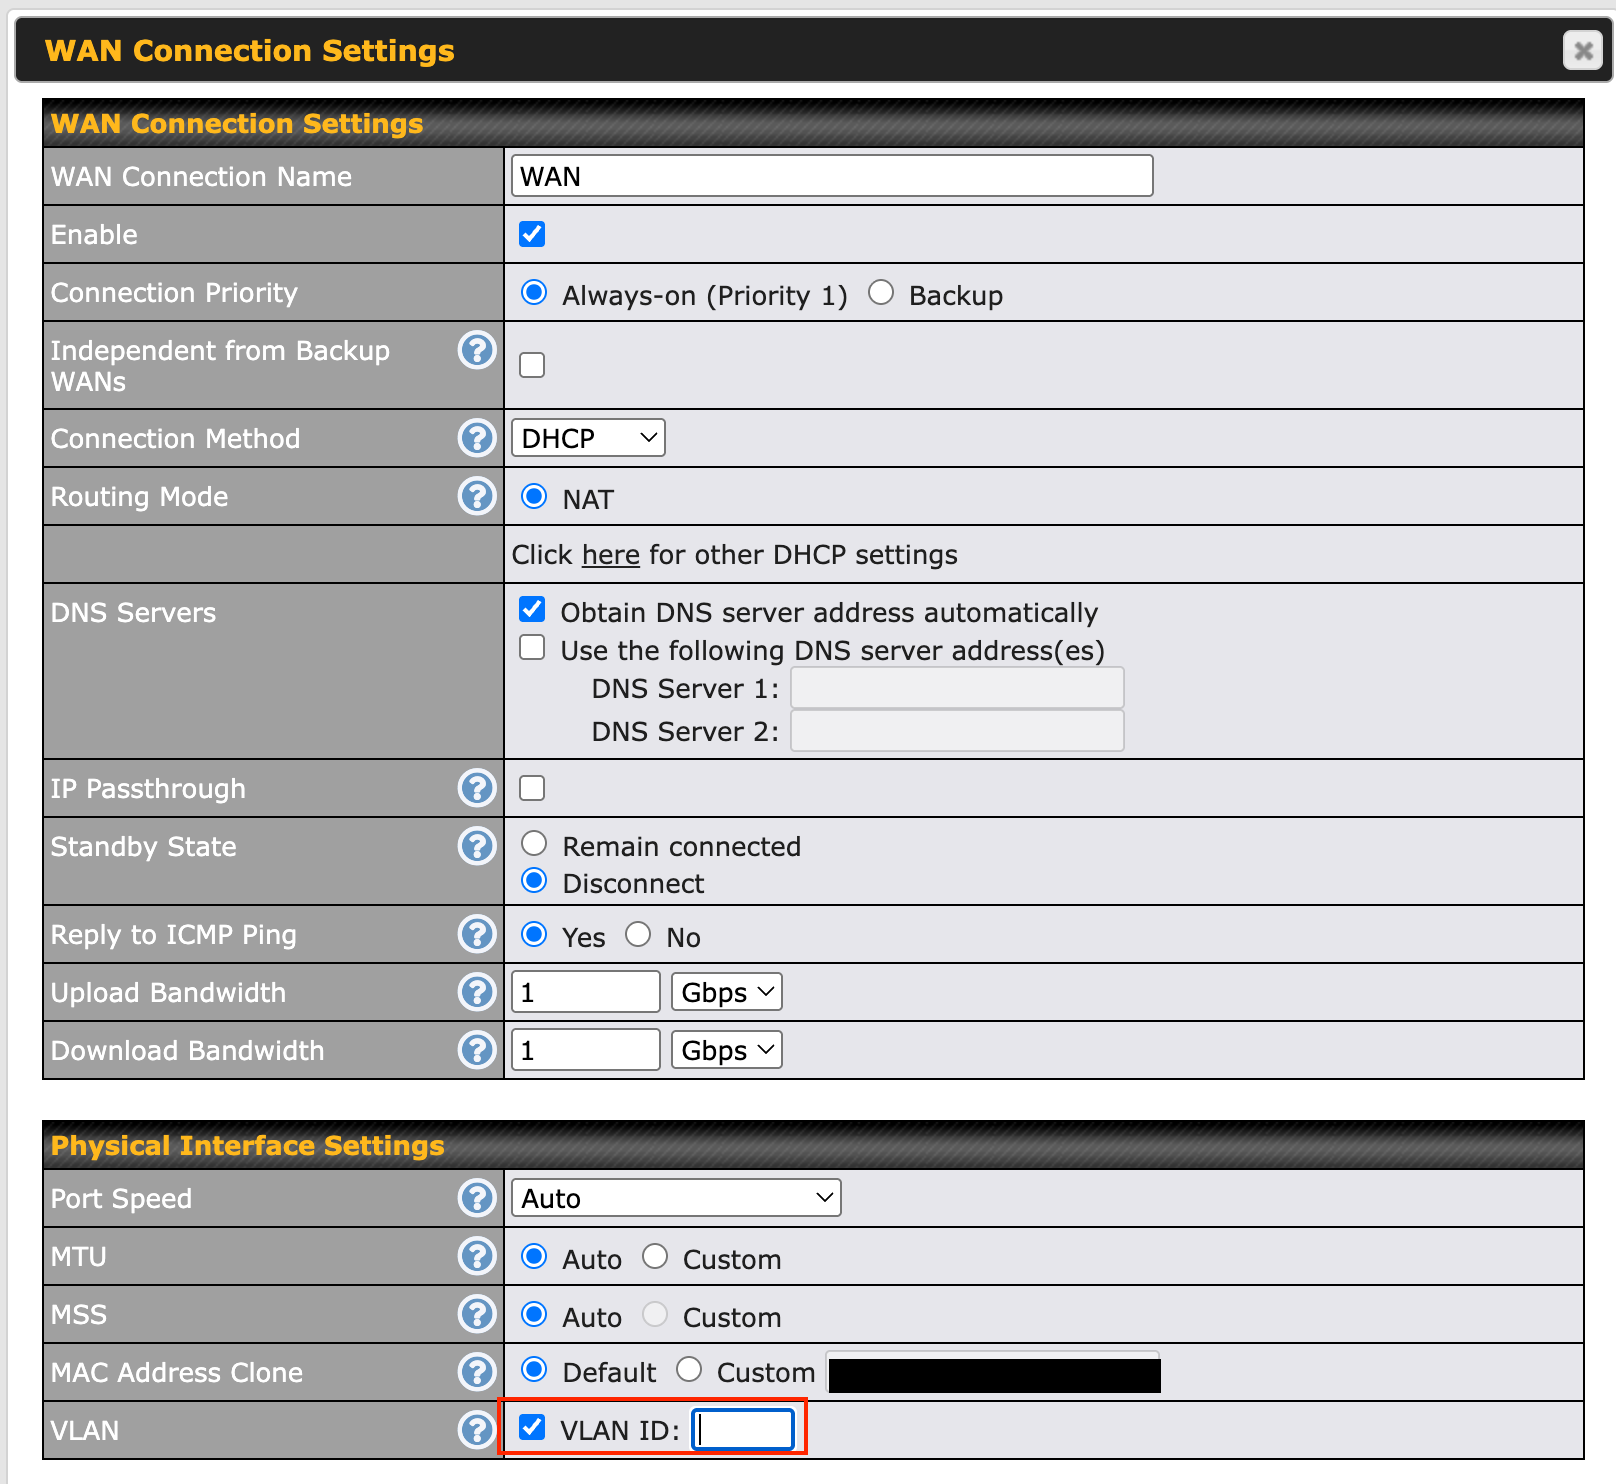
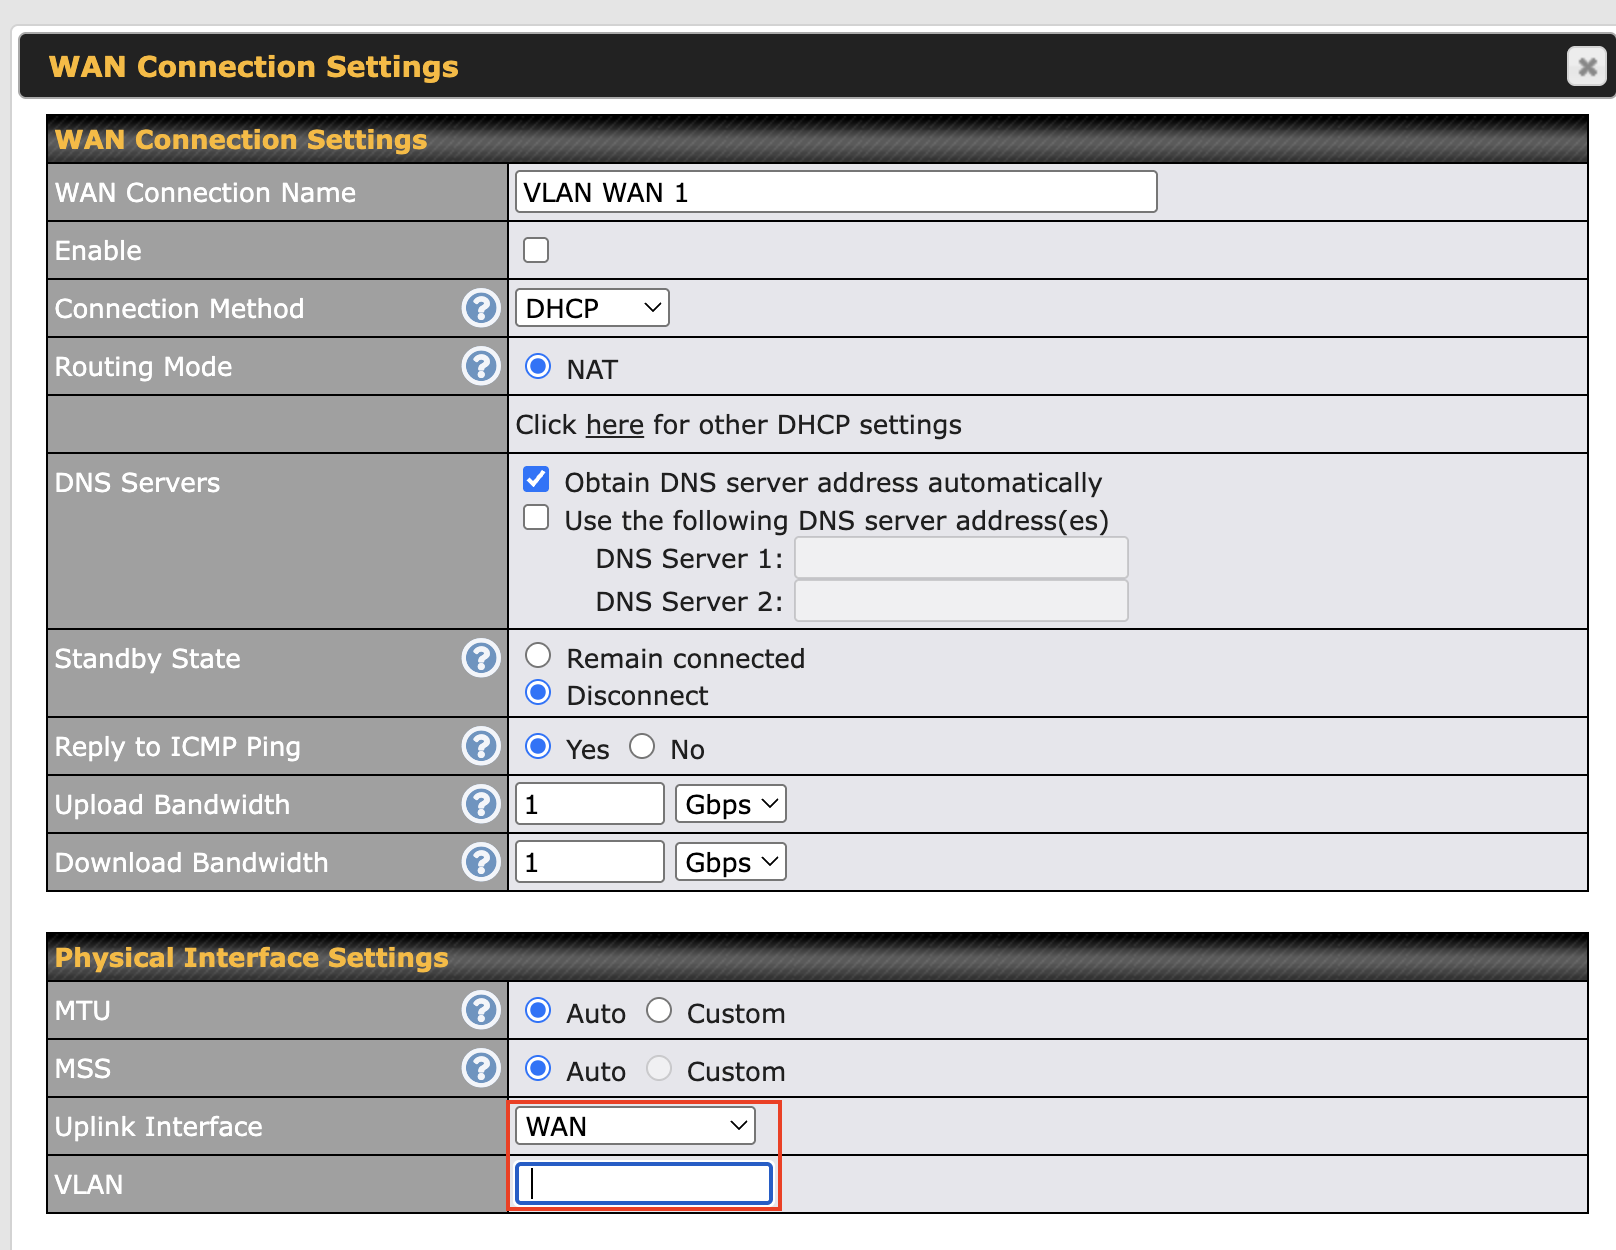
Yes, you should be able to do this assuming that you have the BR2 under a prime care contract or have a license for a VLAN WAN.

The cable would connect to one of the physical WAN ports, you can specify a VLAN tag for that WAN to use for its traffic.

The second one would be configured under a VLAN WAN interface, you would specify the same phsyical WAN port and again just configure the VLAN tag required.

Yes, and yes you either need to use SpeedFusion connect hosted by Peplink to give you somewhere to bond the connections via, or host your own FusionHub, or use another Peplink device.

You should be able to achieve this, however the exact method might depend on what you are using downstream of the Peplink, on the Peplink side you might need to add some VLANs to provide a discrete link to the downstream router, and you can then use outbound policy to direct traffic to each WAN based on something like source IP.

You can configure the WANs to not use NAT, but you would need some other public IPs provided by the ISPs to then use on the LAN side of the Peplink. I.e. each of the transports has say a /31 used as a link net and then the provider routes you a /29 or similar for each transport.

I believe Peplink recently added the ability to support MTUs ≥1500 on the WAN interfaces, but you should check this with a sales partner as it might vary platform to platform.

I’ve personally not tested this, probably need someone from Peplink to confirm what the behaviour is but I do not believe you can set a DSCP value to be added to the tunnel headers, and I would expect that DSCP would either be passed through to the WAN or stripped entirely.

Given that you have a couple of somewhat speciffic requirements here I would suggest you find a Peplink partner in your region to do some pre-sales work with you as they should be able to either provide you a test unit or help you with validating the behaviour to see if it would meet your needs.

2 Likes

Thanks, this was very helpful!